Acts instantly and effectively against ransomware, data exfiltration, infostealers and advanced persistent threats.
Ransomware still disrupts businesses daily, even after a decade of security advances and AI innovation.
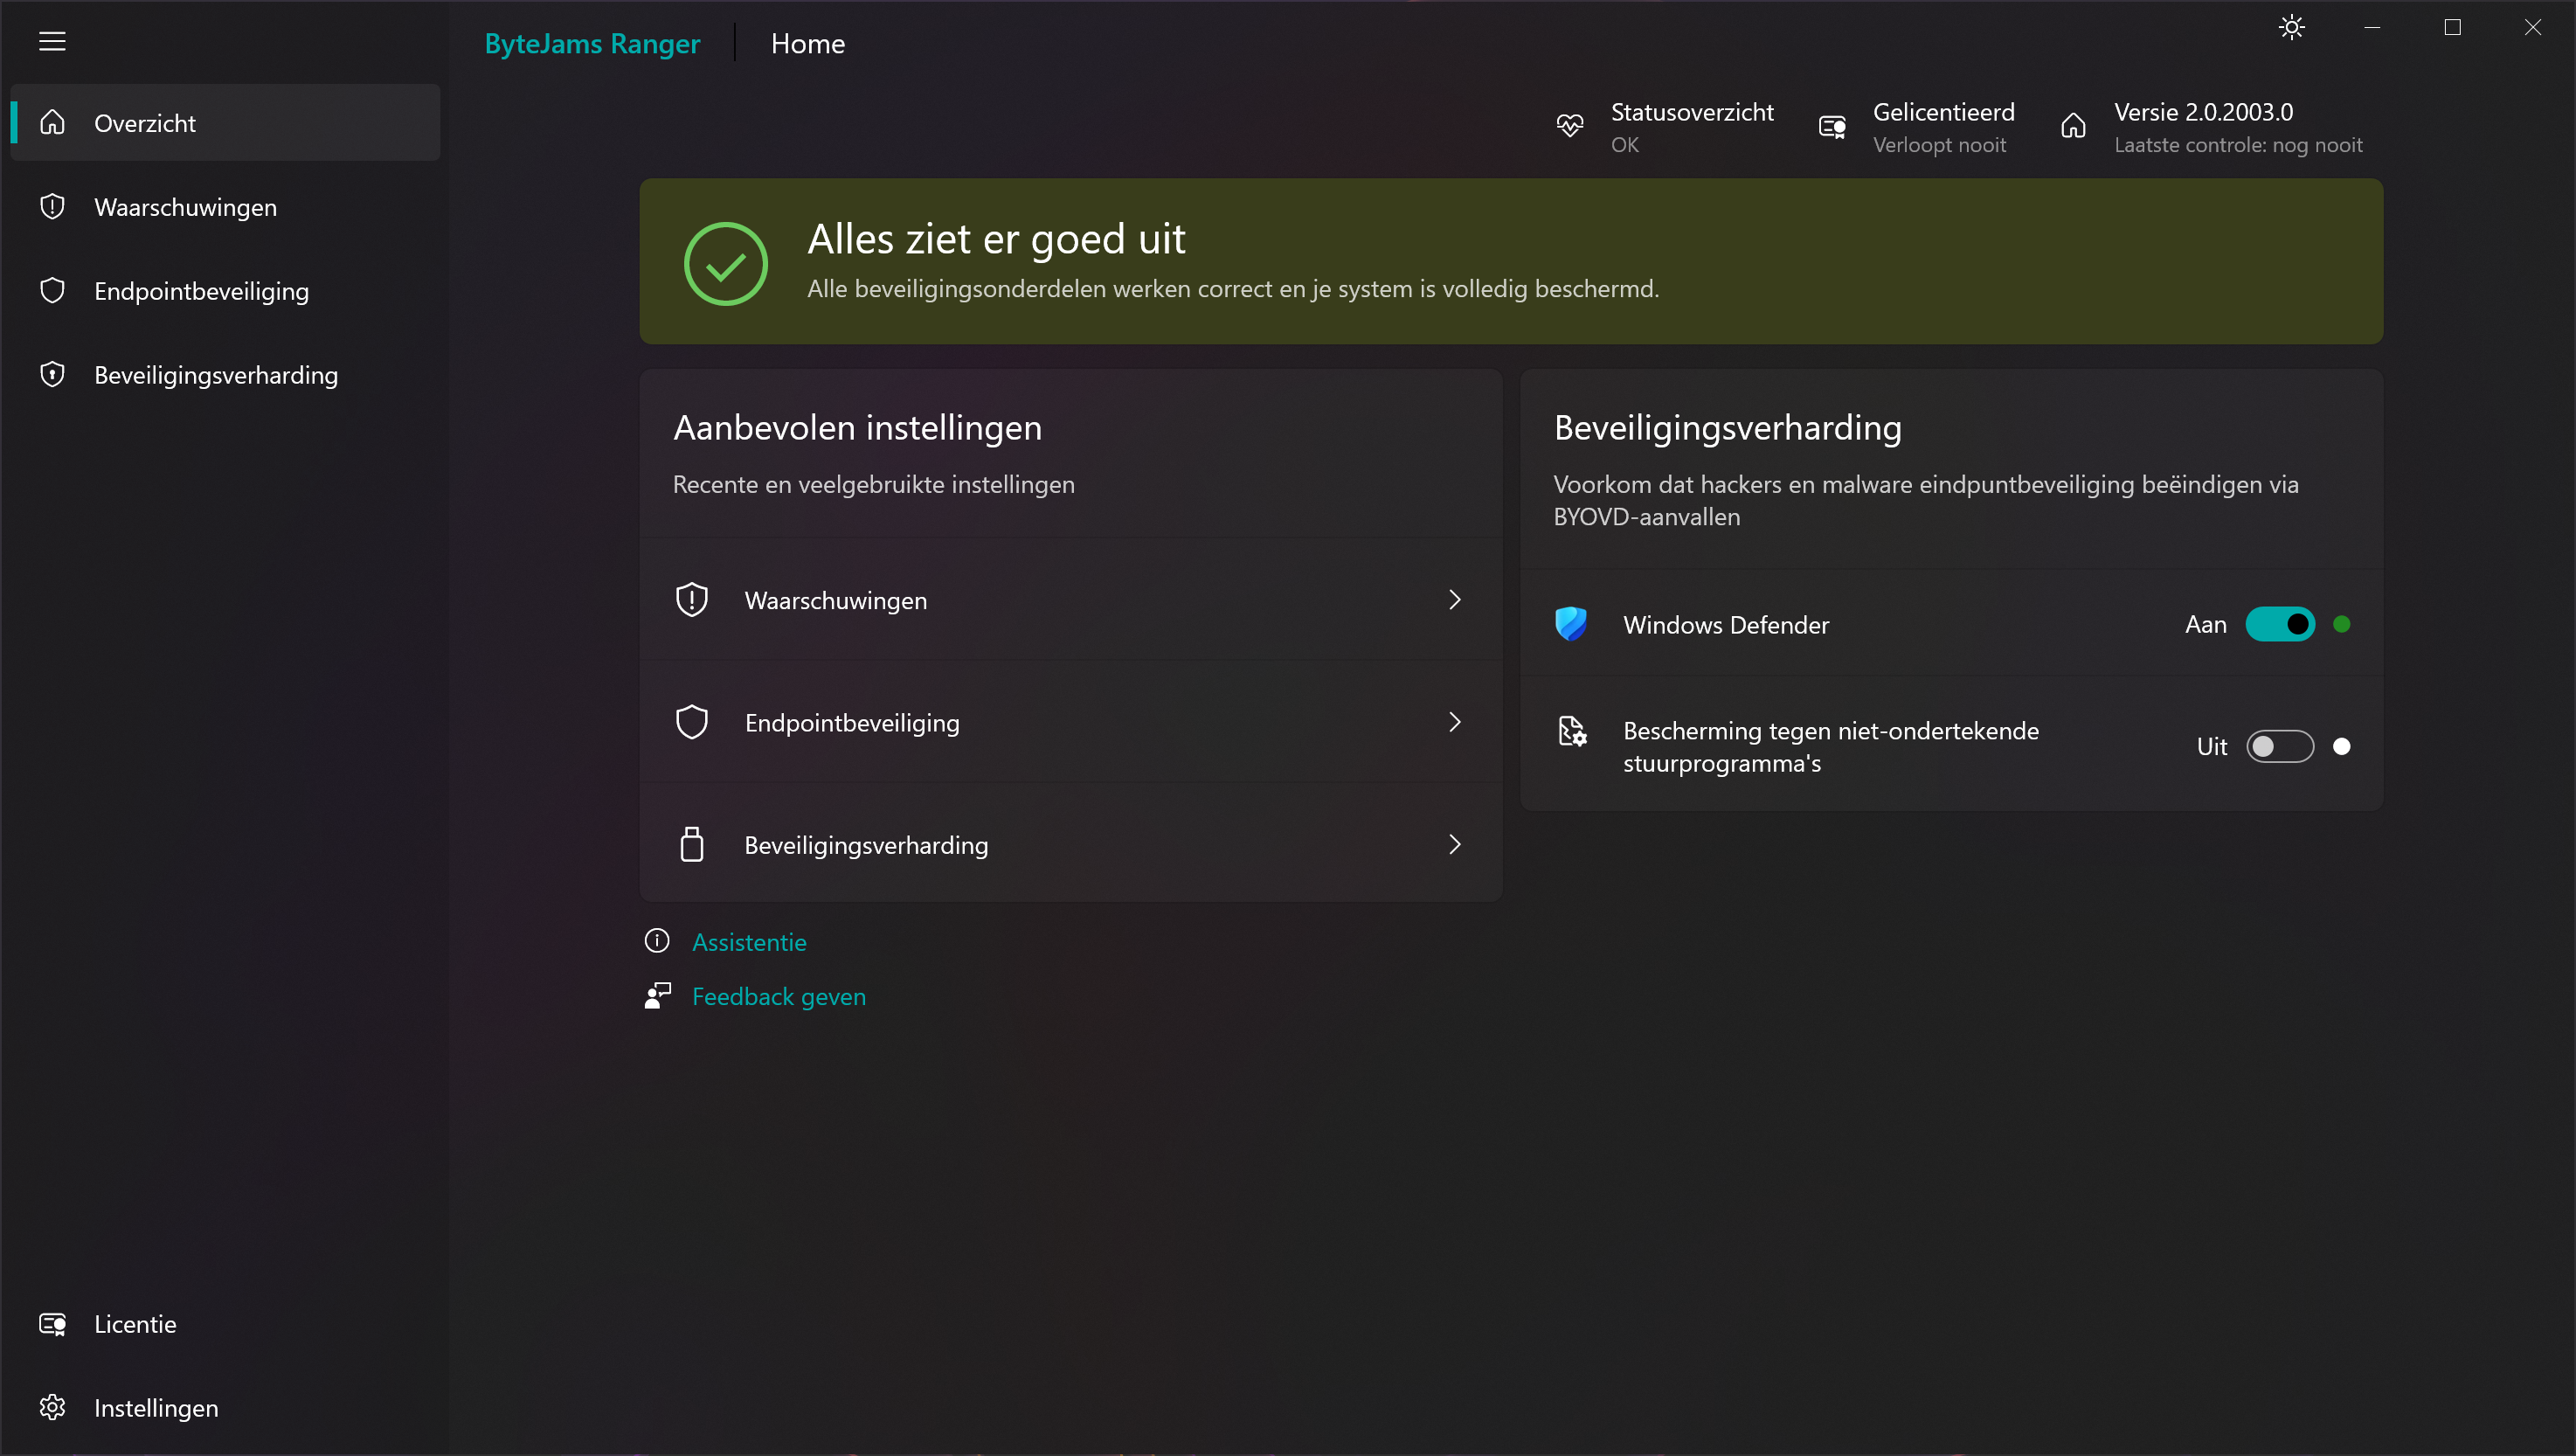
Our lightweight, on‑device ransomware protection works autonomously without relying on threat intelligence or AI, delivering universal file protection, automatic recovery, and securing both local and remote data against encryption attacks, no matter the file size or type.
With double extortion now standard practice, attackers steal files before encrypting them. When the ransom is not paid, they publish your stolen data.
Our autonomous, on‑device technology detects and automatically blocks data exfiltration without signatures or ongoing management, securing intellectual property and limiting breach impact even when attackers gain network access.
Today, over 90% of ransomware attacks originate from unmanaged or compromised devices
(Microsoft
).
Preventing both local and remote ransomware attacks has never been more critical.
Our patented technology not only blocks these threats but also detects data exfiltration, all with a single, unified algorithm.
Microsoft's Windows Resiliency Initiative transitions security providers to user mode for greater stability.
ByteJams Ranger delivers kernel-free ransomware and data exfiltration protection, showcasing our adaptability to evolving security needs.
We block the techniques attackers rely on directly, so you're covered against threats no signature has ever seen.
Your Data Stays in the EU.
Full compliance and privacy: your telemetry never leaves European soil.
Just 3 MB installed: minimal footprint, maximum protection.
Delivered natively in OCSF format, so it drops straight into your existing stack.
Powered by OCSF
Microsoft's latest report confirms data theft drives the vast majority of breaches. Here's why exfiltration, not just encryption, is the threat ByteJams Ranger was built to stop.
Read more →